Key Takeaways
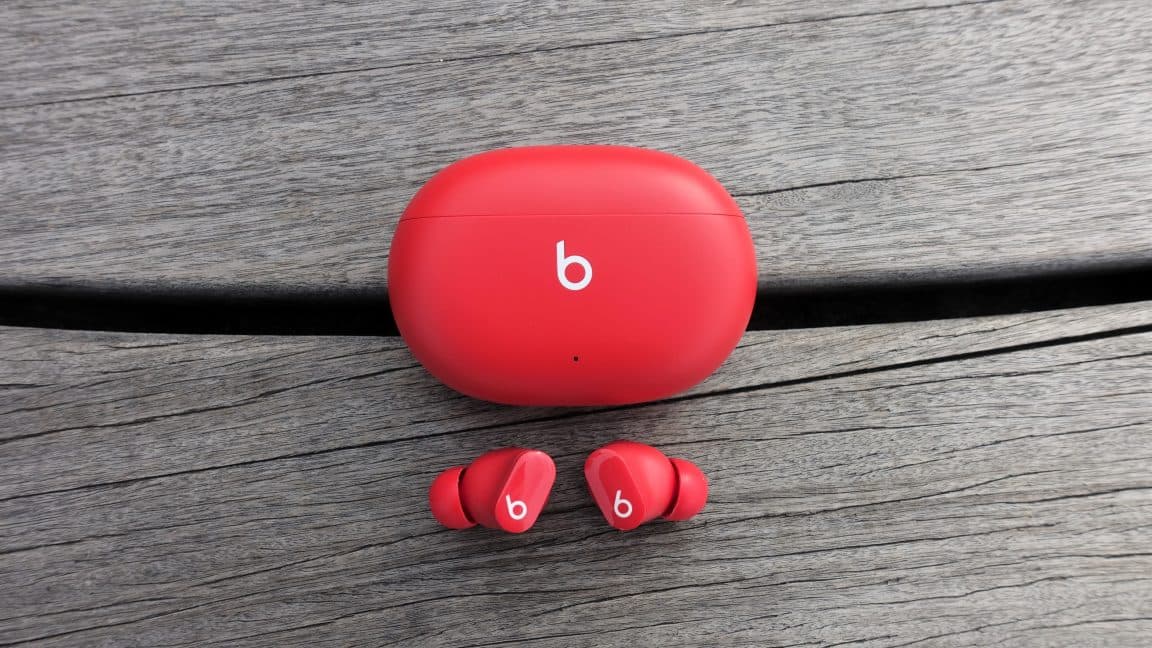
- CVE-2025-20701 allowed attackers within Bluetooth range to impersonate paired devices and eavesdrop through phone microphones
- The fix arrives automatically via Beats Firmware Update 1B211 when earbuds are connected to an Apple device
- The same Airoha chip flaw affects headphones from Jabra, Bose, JBL, and others
Apple has patched a high-severity vulnerability in the Beats Studio Buds that allowed nearby attackers to impersonate previously paired devices and listen in on conversations through a phone's microphone. The flaw, tracked as CVE-2025-20701 and rated 8.8 out of 10 in severity, stems from improper authentication in firmware running on Airoha Bluetooth chips.
Security researchers Dennis Heinze and Frieder Steinmetz of Insinuator discovered the vulnerability last year and demonstrated end-to-end attacks that captured audio within earshot of compromised devices. Apple released the fix Tuesday in Beats Firmware Update 1B211.
How the Beats eavesdropping attack works
The vulnerability exploits a flaw in Bluetooth authentication. An attacker within signal range, typically 10 to 30 meters, can trick the earbuds into believing they're a device that was previously paired. Once that trust is established, the attacker gains access to the connected phone's microphone.
Apple's security advisory put it plainly: "An attacker within Bluetooth range may be able to listen through the microphone of a device which is not yet paired and actively seeking pair requests."
The researchers showed this wasn't limited to passive listening. The full attack chain could retrieve call history, access contacts, and even place calls to arbitrary numbers. These capabilities vary depending on the paired device and its permissions.
Which devices are affected beyond Beats?
The problem isn't Apple-specific. CVE-2025-20701 is one of three vulnerabilities tied to Airoha Systems chips, which power Bluetooth in products from multiple manufacturers. Airoha released an updated software development kit for affected hardware vendors.
Jabra announced patched firmware the same week as Apple. Bose and JBL have also confirmed their devices received fixes. Anyone using Bluetooth earbuds or headphones with Airoha chips should check for firmware updates.
This follows a pattern. In January, researchers disclosed WhisperPair, a separate set of Bluetooth vulnerabilities affecting devices connected via Google Fast Pair. That attack allowed hijacking and geolocation of more than a dozen devices from Sony, Nothing, JBL, OnePlus, and Google itself.
How to check if your Beats are patched
The firmware update delivers automatically when your Beats Studio Buds are paired with and within Bluetooth range of an iPhone, iPad, or Mac. No manual download required.
To verify you have the fix, open Settings on your Apple device, go to Bluetooth, and tap the info button next to your headphones. Look for Beats Firmware Update 1B211 or later.
Should you worry about Bluetooth attacks?
There are few, if any, confirmed cases of these Bluetooth vulnerabilities being exploited in the wild. The attacks are complex. An attacker must stay within Bluetooth range continuously while running the exploit, making opportunistic attacks impractical for most scenarios.
That said, targeted attacks are another matter. Executives, journalists, activists, or anyone handling sensitive information should treat Bluetooth with more caution. Turn it off when not in use. Stay aware that enabled Bluetooth expands your attack surface.
Another recent security breach affecting enterprise tools
Related coverage of high-severity vulnerability patches
The bigger picture for wireless audio security
Bluetooth vulnerabilities keep surfacing because the protocol was designed for convenience, not adversarial environments. Pairing is meant to be quick and painless. Authentication checks are often minimal. When those checks fail, attackers inherit whatever permissions the legitimate device had.
The Airoha chip issue and WhisperPair vulnerabilities both highlight how fragmented the Bluetooth supply chain has become. A single component vendor's firmware flaw can ripple across dozens of consumer brands. Apple, Jabra, Bose, and JBL all ship products with the same underlying weakness.
Frequently Asked Questions
What is CVE-2025-20701?
It's a high-severity vulnerability in Airoha Bluetooth chips that allowed attackers within Bluetooth range to impersonate paired devices and eavesdrop through phone microphones. It affects Beats Studio Buds and headphones from other manufacturers.
How do I update my Beats Studio Buds firmware?
The update delivers automatically when your earbuds are paired and within Bluetooth range of an iPhone, iPad, or Mac. Check your current firmware in Settings > Bluetooth > tap the info button next to your headphones.
Are other headphone brands affected by this vulnerability?
Yes. Jabra, Bose, and JBL have confirmed their devices using Airoha chips were affected and have released patches.
Has this Bluetooth vulnerability been exploited in real attacks?
There are no confirmed reports of active exploitation. The attack requires an attacker to remain within Bluetooth range continuously, making it impractical for most opportunistic scenarios.
How can I protect myself from Bluetooth eavesdropping attacks?
Keep firmware updated, turn off Bluetooth when not in use, and be aware that having Bluetooth enabled expands your attack surface, especially if you handle sensitive information.
Logicity's Take
This patch matters beyond the immediate fix. It exposes how a single chip vendor's authentication flaw can create vulnerabilities across a dozen consumer brands simultaneously. As Bluetooth audio moves upmarket, with premium earbuds now doubling as hearing aids and health monitors, the security stakes rise. Manufacturers need to treat firmware security with the same rigor they apply to their own product code, not just ship whatever the chip vendor provides.
Need Help Implementing This?
If your organization needs guidance on Bluetooth security policies, firmware update management, or vulnerability assessment for connected devices, our team at Logicity can connect you with vetted security consultants. Contact us at hello@logicity.in.
Source: Ars Technica
Huma Shazia
Senior AI & Tech Writer
Produced with AI assistance and reviewed by the Logicity editorial team. Learn more in our Editorial Policy.




